
Ready for the assessor on any day of the year.
Rebasoft populates evidence — asset inventory, secure configuration, user access, patch posture, malware protection — so you review and submit rather than start from scratch. Then it keeps that picture true, so CE+ becomes a continuous state, not a calendar event.
Cyber Essentials is no longer a ‘nice to have’.
For UK businesses it has quietly become a commercial imperative, a public-sector requirement, an insurance lever and a board-level signal.
of common cyber attacks are prevented by the controls measured under Cyber Essentials.
A commercial imperative.
Most B2B procurement now requires CE or CE+ before sign-off. Lose the certification, lose the business.
A public-sector requirement.
Central government contracts, NHS, education and local authority work increasingly mandate CE+.
An insurance lever.
Cyber-insurance premiums and limits are now routinely tied to certified status.
A board-level signal.
“We are continuously CE+ compliant” tells customers, regulators and your own board that the basics are in hand.
Mapped to the Cyber Essentials controls.
The technical controls are evidenced continuously and pre-filled into your self-assessment. Policy and scope answers stay with you — Rebasoft tells you the day the technical reality drifts from them.
Every device, workload, container and cloud asset discovered automatically — the incomplete asset list that fails most assessments becomes a non-event.
Every Windows host measured against the CE secure-configuration controls — local admin, screen lock, default passwords, firewall, account separation — each finding mapped to the Group Policy or Intune setting that fixes it.
Local admins, privileged groups, account separation and dormant accounts scored as an automated pass/fail — the least-privilege answer is the truth, evidenced.
Patch posture measured continuously with vendor-grade Windows KB-to-CVE verification. Critical patches older than 14 days raise an alert.
Anti-malware coverage, definition currency and configuration across the estate — including the corners standard endpoint tools miss.
CE+ isn’t a day in the calendar. It’s a state you stay in.
The problem with CE+ isn't getting it. It's keeping it — and proving it month-to-month instead of scrambling for evidence twelve months later. Rebasoft re-measures every control every day, so drift surfaces the day it happens.
| Today | What it actually means | With Rebasoft |
|---|---|---|
| Annual assessment with manual evidence collection | A panic every 12 months. High consultancy bills. Frequent failures. | Continuous compliance state. Evidence always on. |
| Self-certification at the £300 level | Fine for very small businesses with no B2B exposure. Won't get past procurement at most enterprise customers. | CE+ ready — and ready for the bigger frameworks beyond it. |
| Stand-alone GRC tool | Pretty dashboards, depends on you filling them in. | The dashboard is green because the estate is — measured directly. |
| Patch management tool only | Most CE+ failures are configuration, not patches. | Both patching and configuration measured, reported and fixable from the same system. |
From the blog
Audit Evidence Requirements That Stand Up
Meet audit evidence requirements with continuous, service-led visibility that reduces effort, validates controls and gives leadership answers they trust.
Read article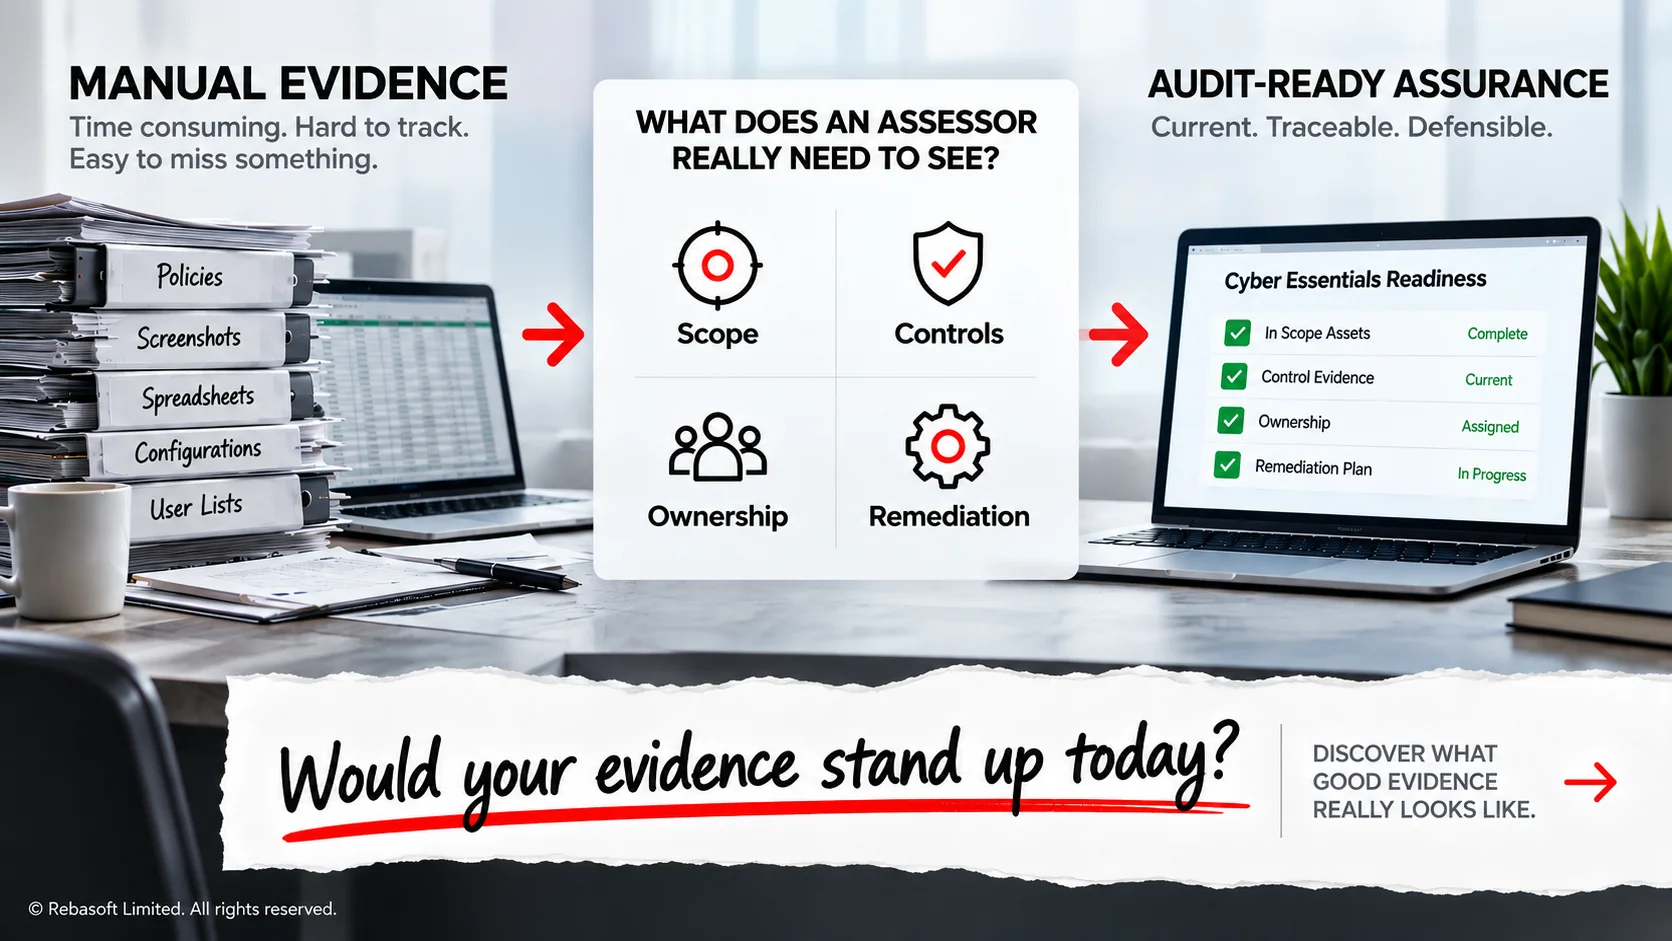
A Cyber Essentials Evidence Example That Stands Up
See a practical cyber essentials evidence example and learn how continuous asset, configuration and access data can reduce audit effort and risk at scale.
Read article
NIST CSF Implementation Guide That Delivers Evidence
A practical NIST CSF implementation guide for turning asset visibility, control evidence and service context into measurable cyber assurance at scale.
Read articleMake your next CE+ assessment a non-event.
A 30-minute walkthrough on a live system. We'll show you the Cyber Essentials Readiness dashboard, the evidence behind it and how to export a full submission.
Does Rebasoft fill in the Cyber Essentials self-assessment for us?
Does Rebasoft replace our CE+ assessor or submit on our behalf?
How quickly can we be CE+ ready?
Does it cover every CE control?
What about non-Windows devices in scope for CE+?
Is this only for first-time certification, or also for renewal?
We're tiny — should we just self-certify?
We're aiming for ISO 27001 or PCI next. Will this still help?
Can MSPs and certification bodies use Rebasoft to deliver CE+ as a service?
More questions? See the full Rebasoft FAQ — answers by topic and by role, or how Rebasoft is priced.