
Which vulnerabilities threaten your critical services?
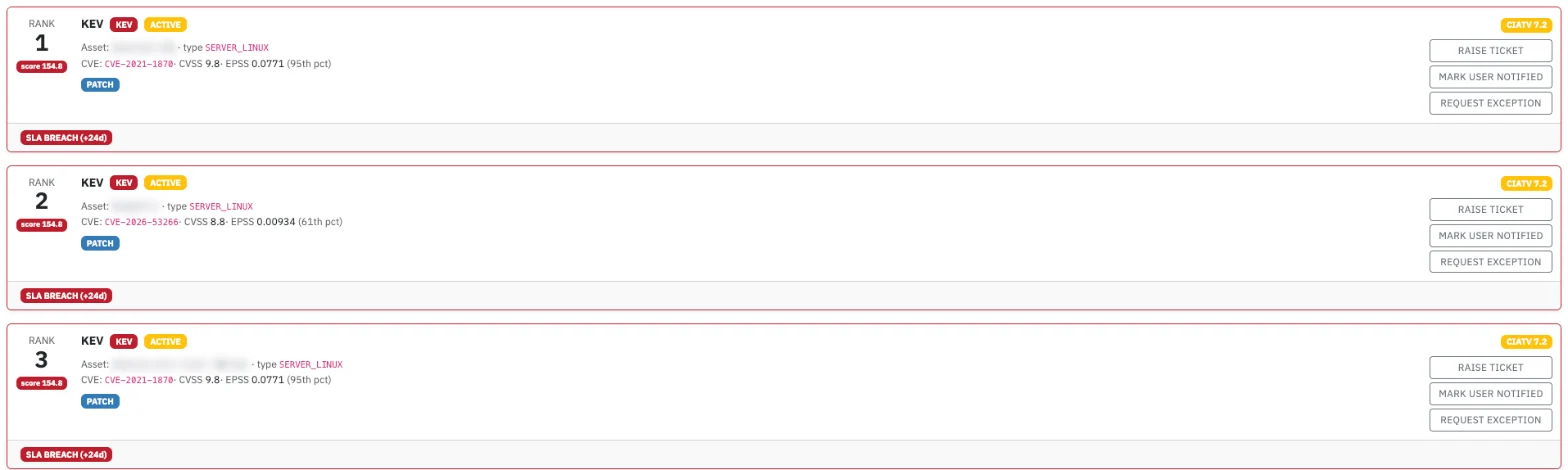
Today’s work, ranked
Each item shows the asset, why it ranks where it does and what to do next, from raising a ticket to requesting an exception.
Findings come from collected evidence, with false positives already filtered
A raw CVE list leaves your team ruling out false positives by hand. Rebasoft takes the software, patch and firmware data it collects, read-only by design, and weighs NVD against the CVE List, Microsoft, distribution advisories, OSV and over 100 vendors. Each finding arrives with its sources, its rule and its status as confirmed or inferred.
Linux backports
When NVD flags sudo and Ubuntu confirms that your build carries the fix, the CVE is removed before it reaches your team. Red Hat, Debian, Oracle, SUSE and Alpine work the same way.
Windows KBs
Installed KBs subtract the CVEs they fix, and older OS-level noise is removed with them.
Network firmware
Device OS versions are matched against vendor data with no agent, and trimmed to the exact build on Cisco and Junos, which cuts the noise on your infrastructure.
Vendor “not affected” statements
A vendor statement removes the NVD match, and the reason remains visible on the finding.
One ranked list, weighted towards known exploitation
Severity alone sends your team to the wrong place first. The Rebasoft score combines KEV, EPSS, CVSS, exposure class, time overdue and the importance your business services pass down. A known-exploited flaw on a web server in a critical service therefore outranks a 9.8 on a test system.
Each card explains why the item is on the list.
Each card sets out what to do next, with text for your service desk.
Your team filters to breaches and records exceptions with a reason and an audit trail.
Hot issues answer “is this one of ours?” site by site
A newly exploited flaw usually means a morning of manual checking. With Rebasoft, KEV additions, EPSS jumps and vendor-critical advisories raise a hot issue, and a single query spans installed software, past findings and network devices.
- 07:40
A firewall flaw is added to KEV
Within hours, a hot-issue card names the flaw in the console.
- 08:15
The analyst opens the drawer
For the selected site, she sees the CVEs, CVSS, the KEV date and EPSS with its seven-day rise.
- 08:16
The first site reads Affected
Each device is listed with days open and SLA state, and a second list shows devices holding the product with no open finding.
- 08:20
The next site reads Can’t tell
The card shows how much of that site has software inventory, so the position is clear.
- 08:25
The report is ready
The position for each site is available as a report, ready to schedule each morning.
A composite of real customer situations. Times are illustrative.
Installed updates close findings with no manual verification
Your team deploys the update through its usual tool, and Rebasoft confirms the KB at the next collection, closes the CVEs it fixes and records the reason. The asset is ranked again and your Cyber Essentials patching figures follow, which ends the chasing and the manual sign-off.
Green means checked
A scanner reports on what it reached. Rebasoft also runs discovery, so it knows which devices remain unassessed. Assets with no software evidence are shown as Not assessed and are not counted as clean.
Evidence-based assessment gives a small team more for less effort
| The usual scanner approach | Evidence-based assessment | What your team gains | |
|---|---|---|---|
| How findings are made | Scans run against targets on a schedule | Collected inventory is weighed against vendor, distribution and NVD data | No scan windows to negotiate and no scanning schedule to manage |
| False positives | Version matches arrive for a person to rule out | Backports, installed KBs and vendor statements are applied first | A shorter list, with the reasons on each finding |
| Coverage | A report covers what the scan reached | Discovery names the devices that were Not assessed | A clear view of coverage, in place of false assurance |
| Priority | Business context is added separately | Importance is inherited from your business services | Work ordered by what the organisation runs on |
From the blog
Attack Surface Management That Reduces Risk
Attack surface management gives leaders continuous visibility and business context to reduce cyber risk, protect critical services and prepare for audit.
Read article
How to Measure Cyber Exposure with Business Context
Learn how to measure cyber exposure by connecting assets, identities, vulnerabilities and controls to the business services that matter most first, now.
Read article
Vulnerability Management Platform Review Criteria
A vulnerability management platform review that cuts through alert volume, tests business context, evidence, coverage, and operational value at scale.
Read articleHow does Rebasoft differ from a vulnerability scanner?
Does Rebasoft patch?
How does this work with Microsoft Defender?
More questions? See the full Rebasoft FAQ — answers by topic and by role, or how Rebasoft is priced.
Bring a CVE and see whether it applies to you
In thirty minutes on a live console, you will see why a finding exists, what ranks first and how coverage is reported.