User access and identity

Replace manual access reviews with evidence you can defend.

Security starts with who holds access. Identity rules surface dormant administrators, MFA gaps and stale guests, and exceptions carry an approver and expiry.
USERS & ACCOUNTS 413 Total accounts 88 Enabled 31 Privileged 28 Privileged w/o MFA BY PROVIDER 413 accounts Local AD Entra PRIVILEGED & MFA 28 w/o MFA CE-ACC-005 ACCOUNT HEALTH 26 / 100 MFA coverage 3 / 88 enabled dormant accounts to review One view across: AD Entra ID M365 Windows local Linux sudoers 28 admins without MFA Who holds what, in one place. Exceptions with an end date.
In the console

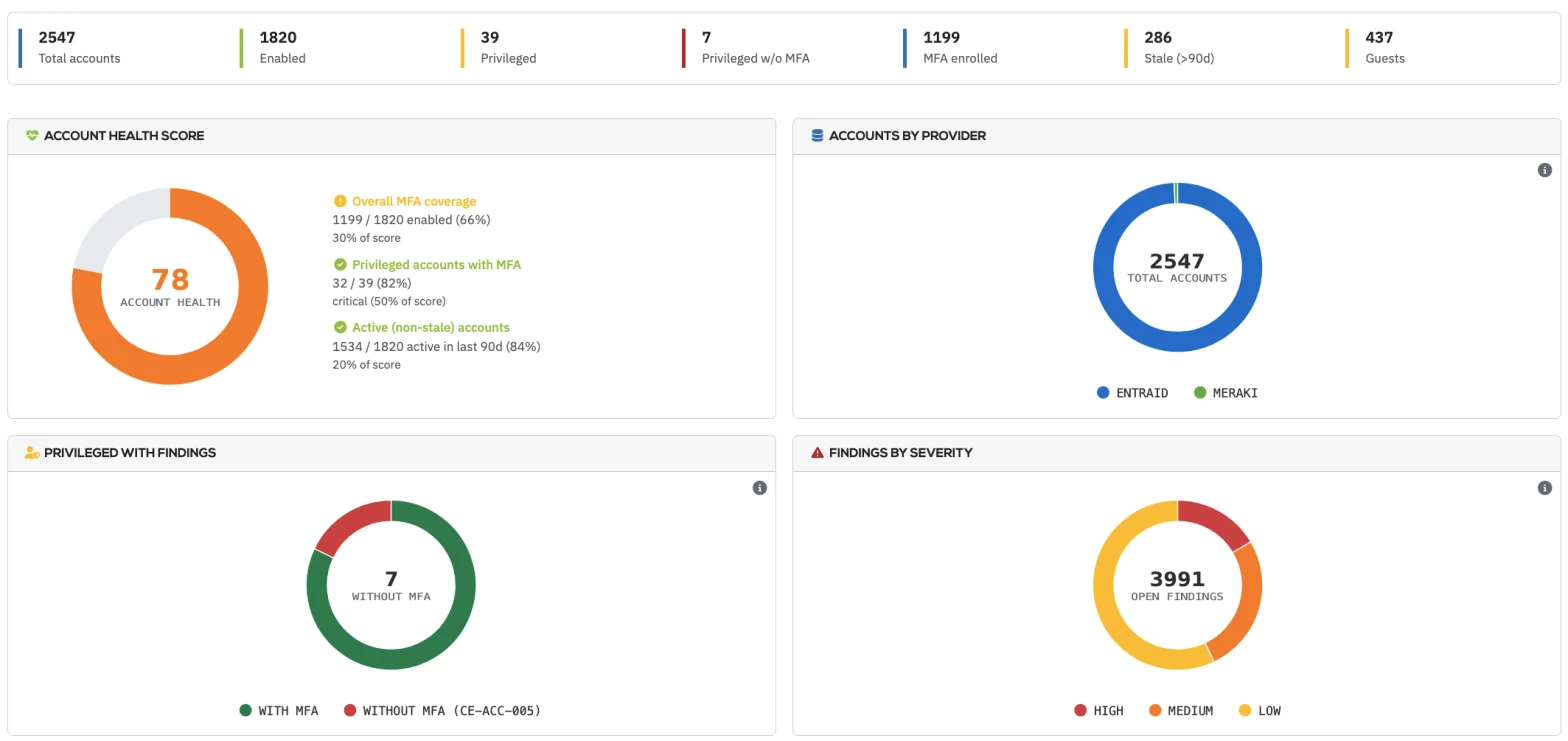
Accounts and findings at a glance

An account health score, MFA coverage, privileged accounts without MFA and stale accounts, with open findings by severity.

Example console view.
See what’s there

Identity rules replace the access review spreadsheet

Exported account lists age quickly and rely on someone reading them line by line. Rebasoft runs these rules against your collected accounts and explains each finding, which cuts review time and reduces what gets missed.

Privilege

Dormant and orphaned administrators, disabled accounts holding privilege, standing administrators where PIM is expected, oversized privileged groups and an enabled built-in administrator.

MFA

Privileged accounts with no MFA registered, and enabled users with none on a provider that supports it.

Guests

Guests in privileged roles, and stale guest accounts.

Service accounts

Service accounts with no owner, and service accounts that can log on interactively.

Hygiene

Enabled accounts with no recent sign-in, passwords past your age limit, and accounts missing ownership details.

An access review in practice

A dormant account resolved, with each decision documented

  1. Monday

    A dormant administrator is identified

    Rule CE-ACC-003 raises an Entra administrator who has not signed in within the tenant’s threshold. The finding names the account and the number of days idle.

  2. Monday

    The threshold is reviewed

    The IT manager previews the effect of a revised threshold before saving it with a reason, and history retains both.

  3. Tuesday

    A break-glass account is confirmed

    The account is meant to remain unused, so she records an exception with the approver, an expiry date and a change reference. The finding is suppressed and the suppression is logged.

  4. Tuesday

    Two leavers are removed

    Two further dormant administrators belong to former staff. She removes their roles in Entra, and the next collection closes both findings.

  5. Expiry date

    The exception lapses

    The exception stops applying on the date she set. If the account remains dormant, the finding returns for review.

A composite example based on product behaviour. The default dormancy threshold is 30 days.
Fix what matters

Exceptions your auditor can follow

Exceptions kept in email are hard to defend at audit. Rebasoft holds the reason, approver and end date beside the finding, which gives the next review a clear starting point.

Why
Reason

The justification for the exception.

Who
Approver

The person named as approving it.

Until
Expiry

The date the exception stops applying.

Ref
Change reference

The reference to your own change process.

Prove it

Access reviews that stand up to audit, site by site

Thresholds with history

Preview a change, save it with a reason and retain the history.

Findings with a lifecycle

Raised, reopened and resolved, with trends over time.

Reports per site

Schedule the users and accounts report for each site, so that local managers receive their own view.

Evidence you can rely on

Green means checked

An empty findings list should never be mistaken for a clean one. The user access control passes when its evidence is complete and current. Otherwise Rebasoft reports Not assessed and gives the reason.

Patching412 of 412 devices checked
Pass
Malware protection3 devices with no protection
Fail
Secure configuration38 devices unreachable: credential rejected
Not assessed
Illustrative example
FAQ
Which accounts does it cover?
Rebasoft brings accounts from Active Directory, Entra ID and Microsoft 365 together with local accounts on Windows and Linux, which ends the hunt across consoles.
Do we need an agent to see local administrators?
No. Rebasoft uses native operating system access and the credentials you provide, so there is nothing to deploy.
Does Rebasoft change any accounts?
No. Rebasoft is read-only by design, so your directories stay exactly as they are and your team stays in control of each change.
What does setup involve?
Setup is simple: read access to your directories and hosts, and read permissions for Microsoft Graph. The connection test confirms what is available.
Does it support Cyber Essentials?
Yes. The rules feed the user access control in the Cyber Essentials verdict, so access evidence is ready when your assessor asks.

More questions? See the full Rebasoft FAQ — answers by topic and by role, or how Rebasoft is priced.

See identity evidence on a live console

In thirty minutes, see the rules, a live finding and the exception register, and how much of your access review they replace.