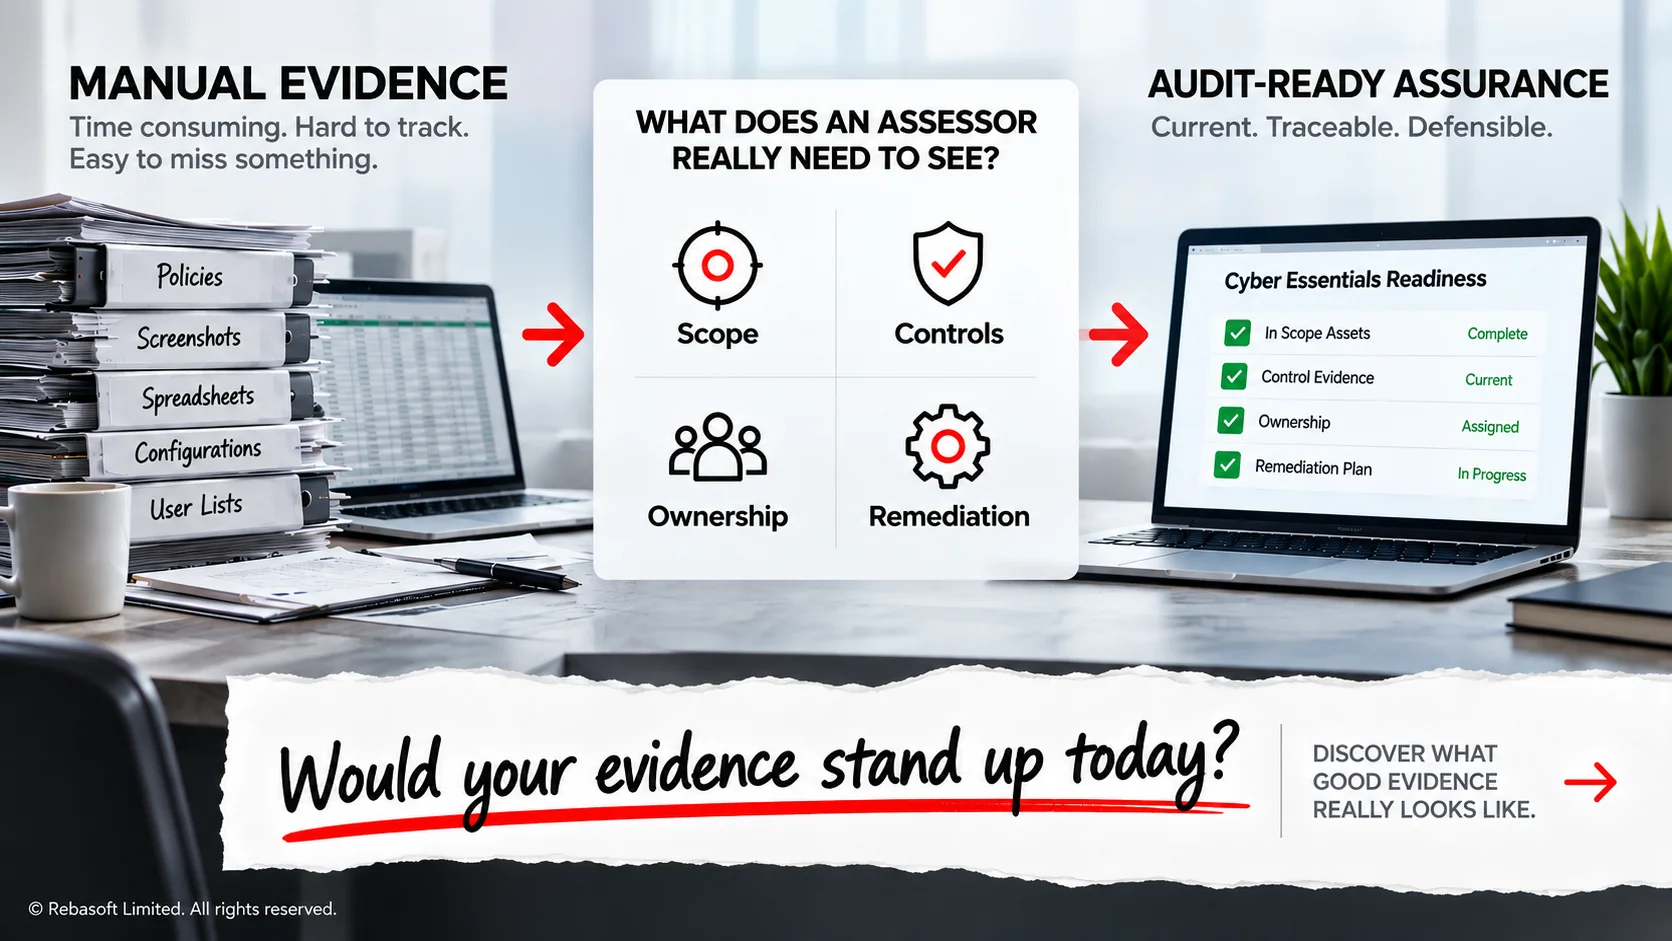
An auditor asks for proof that privileged access is reviewed, critical systems are configured securely and exceptions are being managed. Too often, the answer sits across spreadsheets, ticket queues, screenshots and the knowledge of a few overstretched people. Compliance assurance software replaces that scramble with current, defensible evidence - connected to the services the organisation relies on.
For regulated organisations, compliance is not a once-a-year project. Controls can drift between audits, new assets can appear outside approved processes, and a change in identity or configuration can create exposure long before anyone notices. Leadership needs more than a statement that policies exist. They need answers they can trust about whether controls are operating, where they are weak and what needs attention first.
What compliance assurance software should deliver
Compliance assurance software should turn technical activity into a clear view of control effectiveness. That starts with accurate visibility. An organisation cannot assure a control over devices, cloud services, identities or applications it does not know exists.
The right platform continuously identifies the assets, accounts, services and configurations that matter, then maps them to control requirements and business context. It should show whether a control is passing, failing or unsupported by evidence, rather than forcing teams to interpret disconnected alerts from separate tools.
This changes the purpose of compliance reporting. Instead of producing a static record of what was believed to be true at a point in time, teams can provide evidence that reflects the current environment. Auditors gain a clearer trail. Security teams spend less time collecting proof. Executives can see the risk behind a compliance gap, not just a percentage on a dashboard.
That distinction matters when a critical business service depends on a system with an insecure configuration, an unpatched vulnerability or excessive access. The issue may affect a control score, but its real significance is the potential disruption to operations, customers or public services.
Why periodic evidence is no longer enough
Many compliance processes still rely on periodic reviews. A quarterly access review, a monthly vulnerability export or a pre-audit evidence exercise may satisfy a timetable, but it does not provide continuous assurance.
Between those checkpoints, infrastructure changes. Cloud resources are created and retired. Endpoint estates expand. Users change roles. Third parties gain access. Security configurations drift as updates, workarounds and operational pressures accumulate. A control that passed last month may no longer be effective today.
This is where organisations can confuse compliance activity with risk reduction. Completing a review proves that a review happened. It does not necessarily prove that the underlying estate remains controlled.
Continuous assurance closes that gap by monitoring the state of relevant assets and controls over time. It creates evidence as part of normal operations, rather than demanding a manual evidence campaign when an audit date approaches. The outcome is more than faster reporting. It is earlier visibility of control failure, with time to fix it before it becomes an incident, audit finding or insurance concern.
Start with service context, not control checkboxes
A long list of failed checks is not a prioritisation strategy. Security and compliance teams need to know which failures expose the services the business cannot afford to lose.
A useful compliance assurance platform connects assets and identities to business services, owners and dependencies. This lets teams distinguish between a low-impact issue on a retired test server and the same issue on infrastructure supporting payroll, patient care, financial transactions or a public-facing service.
This context also improves conversations with leadership. Rather than reporting that 400 devices have a configuration exception, a CISO can explain which services are affected, whether compensating controls exist, who owns remediation and what residual risk remains. That is the level of information boards, regulators and insurers expect.
There is a trade-off. Building meaningful service context requires ownership data and a willingness to improve records that may be incomplete. But this effort pays back quickly. Without context, teams either treat every finding as urgent or rely on intuition to decide what can wait. Neither approach scales in a complex estate.
The evidence model matters as much as the dashboard
Not all compliance evidence is equally useful. Screenshots and manually exported reports can be valid, but they are difficult to repeat, easy to misfile and quickly out of date. They also create a dependency on the individuals who know where evidence lives and how it was produced.
A stronger model records the source, time, scope and status of each control observation. It should allow teams to trace a reported position back to the affected asset, identity, configuration or service. Where exceptions are accepted, the record should show who accepted them, why, for how long and what compensating control applies.
That level of traceability helps in two directions. Auditors can test the evidence without repeatedly returning to operational teams. Internal teams can identify whether a recurring failure reflects a technical problem, an ineffective process or a control that no longer fits the environment.
Evidence also needs to be practical. A platform that produces vast quantities of raw data but no clear control narrative simply shifts the burden from collection to interpretation. Good assurance reporting should make it straightforward to answer four questions: what is the control objective, what evidence supports it, where are the gaps, and who is accountable for fixing them?
Reduce audit effort without treating audit as the goal
Audit preparation often consumes weeks of effort because evidence is distributed across IT operations, security, identity, cloud and service management teams. Requests arrive late, formats vary and gaps are discovered when there is little time left to address them.
Compliance assurance software can reduce this effort by keeping evidence organised and current throughout the year. Control owners can see their position before the audit window. Compliance teams can identify missing evidence early. Auditors receive clearer, more consistent material.
However, automation should not be mistaken for automatic compliance. Some controls require judgement, interviews, approval records or physical checks. Others depend on policy interpretation that differs by sector, geography or contractual obligation. The platform should support those workflows and make evidence easier to govern, not claim that every obligation can be reduced to a technical test.
The best result is a more disciplined assurance process: automated where technology can verify facts, accountable where people must make decisions, and transparent where risk has been accepted.
Consolidation improves control confidence
Fragmented tooling creates blind spots. One system may know about vulnerabilities, another about device inventory, another about cloud configuration and another about identity. If those views are not connected, it is difficult to establish whether a control is effective across the estate.
Consolidation does not mean replacing every specialist tool immediately. It means creating a reliable assurance layer that brings key evidence together, identifies overlap and exposes the gaps between systems. This is particularly valuable for organisations managing Microsoft 365, Azure, AWS, Kubernetes, Active Directory, Intune and on-premises infrastructure at the same time.
An agentless and scanless approach can be especially useful where endpoint agents are difficult to deploy, operational technology must be handled carefully, or scanning creates capacity and change-control concerns. It depends on the environment and available data sources, but reducing dependence on intrusive collection methods can speed deployment and broaden visibility.
For MSPs and MSSPs, a consolidated model also supports consistent service delivery across customers. It becomes easier to provide regular assurance reporting, demonstrate control status and focus remediation effort where it will reduce the most risk.
What to look for in a platform
When assessing compliance assurance software, buyers should test whether it can answer operational questions rather than simply display framework labels. Can it discover unknown assets and identities? Can it validate controls continuously? Can it relate findings to a business service and accountable owner? Can it retain evidence and exceptions in a form an auditor can test?
It should also support the reporting needs of different audiences. Operational teams need actionable findings with enough detail to resolve them. Compliance managers need control coverage, evidence status and exception tracking. Executives need a concise view of material exposure, progress and residual risk.
Deployment speed matters, but so does data quality. A quick proof of value is useful only if the platform can maintain an accurate view as the estate changes. Ask how it handles duplicate data, unknown ownership, disconnected systems and incomplete service mappings. These are not edge cases. They are the conditions most organisations are trying to improve.
Rebasoft approaches assurance as a continuous operational discipline, bringing asset, service, vulnerability, configuration and identity intelligence into one environment. The objective is not to generate more alerts. It is to give teams evidence they can act on and leadership answers they can defend.
The strongest compliance position is built before the auditor arrives: clear ownership, current evidence, controlled exceptions and a practical understanding of which gaps could interrupt the services that matter most.