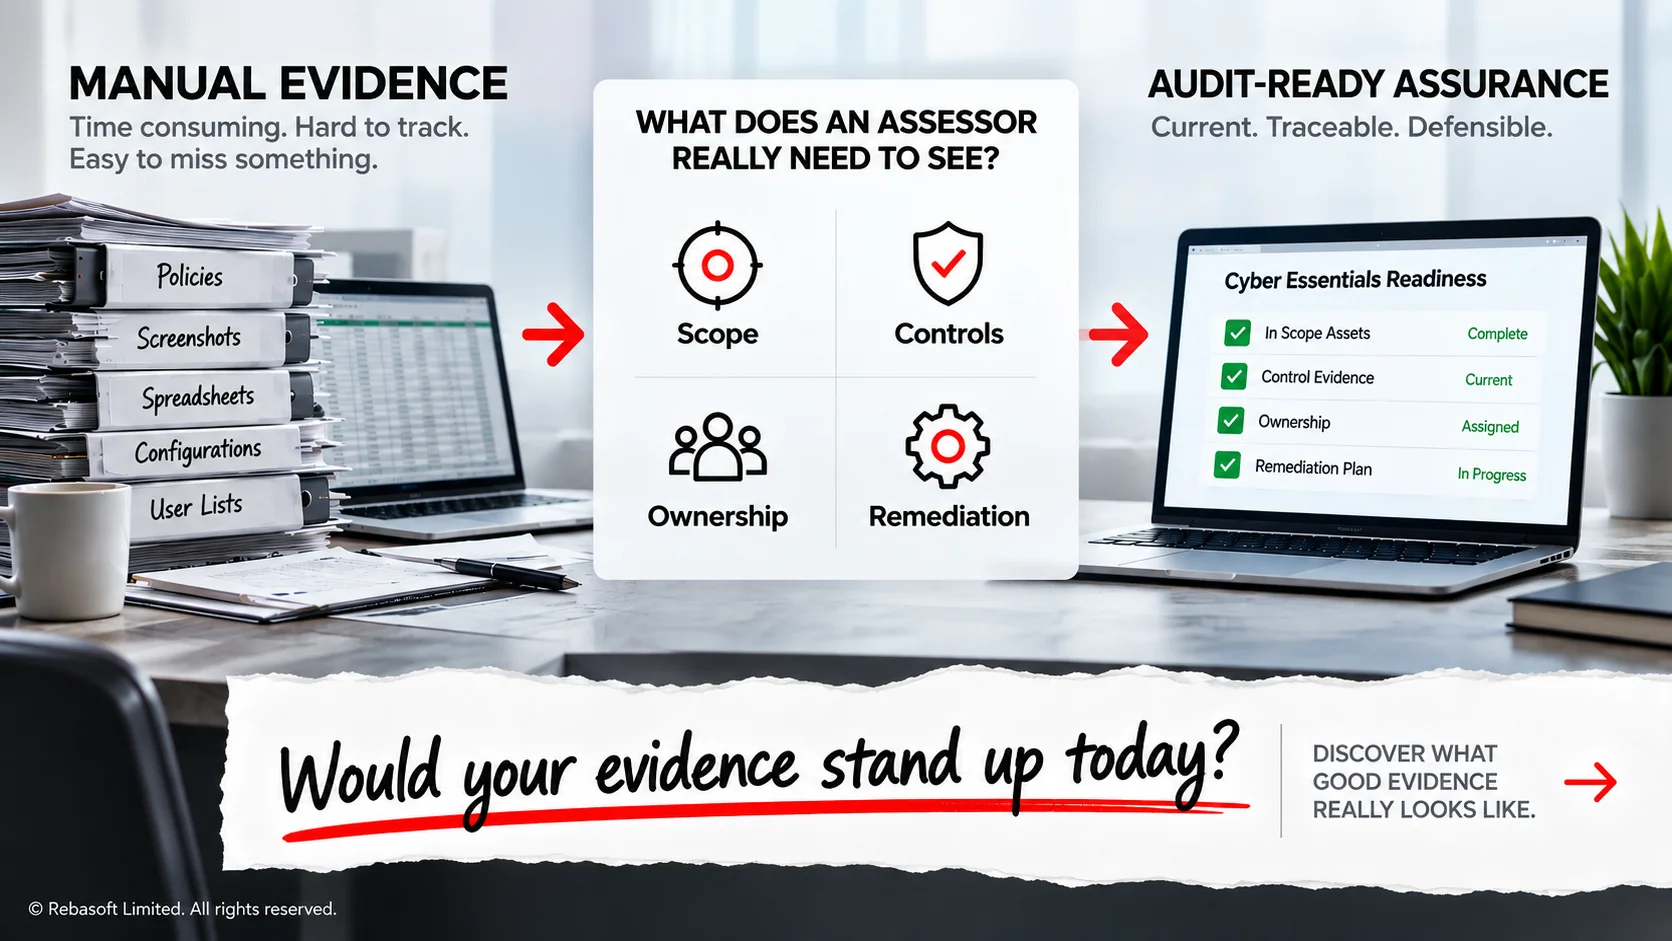
An auditor asks for proof that a privileged account was reviewed, a critical server was patched or an access control operated as designed. Too often, the response is a spreadsheet assembled under pressure, a selection of screenshots and a promise that the process normally works. Audit evidence requirements are not met by producing more documents. They are met by producing reliable proof that can be traced to the control, the asset, the service and the period under review.
For organisations operating under regulatory scrutiny, this distinction matters. Weak evidence extends audits, consumes specialist time and can expose a more serious problem: leadership does not have a dependable view of whether the controls protecting important business services are actually working.
What audit evidence requirements really demand
Audit evidence is the information an auditor uses to reach a conclusion. Its form varies. It may be a system record, configuration state, access log, change approval, vulnerability result, policy attestation or an independently observed test. But the format is less important than the qualities it must demonstrate.
Evidence must be sufficient and appropriate. Sufficient means there is enough of it to support the conclusion, considering the risk and the population being tested. Appropriate means it is relevant to the control objective and reliable enough to trust. A screenshot of a compliant configuration may be relevant, for example, but it is weak evidence if nobody can show which device it came from, when it was taken or whether it represents the wider environment.
Auditors will also look for completeness, accuracy, timeliness and traceability. They need to understand what was tested, who performed or approved the activity, the timeframe covered and how exceptions were identified and handled. Evidence that arrives late, cannot be reproduced or has been manually altered will attract scrutiny, even where the underlying control is sound.
The practical test is simple: could an independent person follow the evidence back to the original source and reach the same conclusion? If not, the organisation has an evidence gap rather than an audit-ready control.
Start with business services, not a pile of controls
Many audit programmes begin with a framework checklist. That is necessary, but it is not enough. A control only has meaning in the context of the service, information or operational outcome it protects.
Consider multi-factor authentication. An organisation may report high adoption across its estate, yet still have an exception on the identity platform that supports payroll, patient records or a revenue-generating customer service. The percentage looks reassuring. The business risk is not.
A stronger approach maps controls to the business services that depend on them. Identify the applications, infrastructure, identities, data stores and third parties that enable each critical service. Then establish the control objectives that matter most: authorised access, secure configuration, vulnerability remediation, monitored change, recoverability and resilience.
This changes evidence gathering from a broad exercise in proving activity into a focused process of proving that the most important services are protected. It also gives auditors and senior stakeholders a clearer explanation of why a finding matters, who owns the response and what should be fixed first.
Build evidence into normal operations
Evidence gathered only at audit time is usually expensive, incomplete and difficult to defend. Teams chase asset owners, extract reports from several tools and reconcile conflicting records. The work may satisfy a short-term request, but it does not improve assurance.
The better model is continuous evidence collection. Each control should have a defined evidence source, owner, collection frequency, retention period and exception process. Where possible, the source should be the system that performs or records the control rather than a manually created report.
For example, secure configuration evidence should show the current state of relevant devices and cloud services, the policy baseline being tested, the date of assessment and the exceptions raised. Patch management evidence should connect discovered vulnerabilities to affected assets, remediation status and the risk posed to the services those assets support. Access reviews should establish the population of accounts, the review decision, the reviewer and the action taken where access was removed or retained.
Automation reduces the administrative burden, but it does not remove the need for judgement. A daily configuration check may be appropriate for internet-facing infrastructure, while a quarterly review could be proportionate for a low-risk internal system. The evidence design must reflect the risk, rate of change and regulatory obligation.
Know which evidence is stronger
Not all evidence carries the same weight. Evidence generated directly by a controlled system is generally more dependable than a manually maintained spreadsheet. Records that are timestamped, access-controlled and retained in their original form are easier to defend than evidence copied between teams.
That does not mean auditors reject manual evidence. A signed review record or management assessment may be entirely valid where human judgement is central to the control. The issue is whether the record can be verified and whether it demonstrates that the stated activity genuinely occurred.
Evidence becomes weaker when it is:
- based on an incomplete or unknown asset population
- collected after the fact without a clear audit trail
- reliant on screenshots with no source, timestamp or scope
- disconnected from the policy or control objective it is meant to prove
- unable to show how exceptions were assessed, approved and resolved
A useful discipline is to retain both the result and the context. A report showing that 95 per cent of devices comply with a baseline is not enough by itself. Preserve the rule tested, the assets included and excluded, the owner of the exception, the compensating control where one exists and the remediation target date.
The asset inventory is part of the evidence chain
A control cannot be evidenced reliably if the organisation does not know what should be under that control. Unknown devices, unmanaged cloud workloads, orphaned accounts and shadow services create a gap between the stated population and the real environment.
This is why asset and service intelligence should sit at the centre of audit readiness. Before reporting on patch compliance, confirm the devices in scope. Before claiming privileged access is reviewed, confirm the identity sources, service accounts and administration paths are known. Before evidencing resilience, confirm the systems supporting the critical service have been identified.
Fragmented tooling makes this harder. One platform may report endpoint posture, another cloud configuration, another identity activity and another ticket closure. Each may be useful, but separately they leave teams to perform the correlation manually. The risk is not simply wasted effort. It is that evidence supports isolated technical statements while failing to answer the auditor's real question: are the controls working across the service that matters?
Treat exceptions as evidence, not embarrassment
No sizeable organisation is fully compliant at every moment. Auditors understand this. What they will question is whether exceptions are hidden, poorly understood or allowed to persist without ownership.
Good evidence shows the exception population clearly. It distinguishes an accepted risk from an overdue remediation, records who approved the decision and identifies any compensating controls. It also demonstrates follow-through. If a vulnerability was accepted for 30 days, the record should show whether it was remediated, renewed through the right governance route or escalated when the deadline passed.
This is where business context improves assurance. A high-severity finding on an isolated test system may require a different response from a lower-severity weakness affecting a public-facing service. Neither should be ignored, but priorities should be explicit and defensible. Leaders need to see both the technical state and the operational consequence.
Make evidence usable for both auditors and leadership
Auditors need detail. Boards and executive teams need confidence that material risks are understood and controlled. These are different views of the same evidence, not separate reporting exercises.
Operational teams should be able to drill from a board-level assurance statement into the underlying assets, users, controls and exceptions. Leadership reports should explain exposure in business terms: which services are affected, whether required controls are operating and what decision or investment is needed. Technical data without this translation creates noise, while executive summaries without traceable detail create false confidence.
An integrated platform such as Rebasoft can help establish this chain by connecting asset, identity, configuration and vulnerability intelligence to business-service context. The value is not another dashboard. It is the ability to produce current, traceable evidence without asking teams to rebuild the story for every audit request.
A practical evidence standard for every control
For each key control, document a short evidence specification. State the control objective, the systems and population in scope, the evidence source, collection frequency, owner, retention expectation and exception route. Then test it from an auditor's perspective before the audit begins.
Ask whether the evidence proves operation over time rather than at one point in time. Ask whether it can be tied to a complete asset and identity population. Ask whether exceptions have accountable owners and whether the output explains the impact on critical services. If any answer is unclear, improve the evidence process before relying on it in a formal assurance statement.
The most credible audit evidence is not created in a rush before fieldwork starts. It is produced every day by well-understood controls, connected to the services the organisation cannot afford to lose. That is how audit effort falls, assurance becomes more credible and leadership receives answers it can trust.