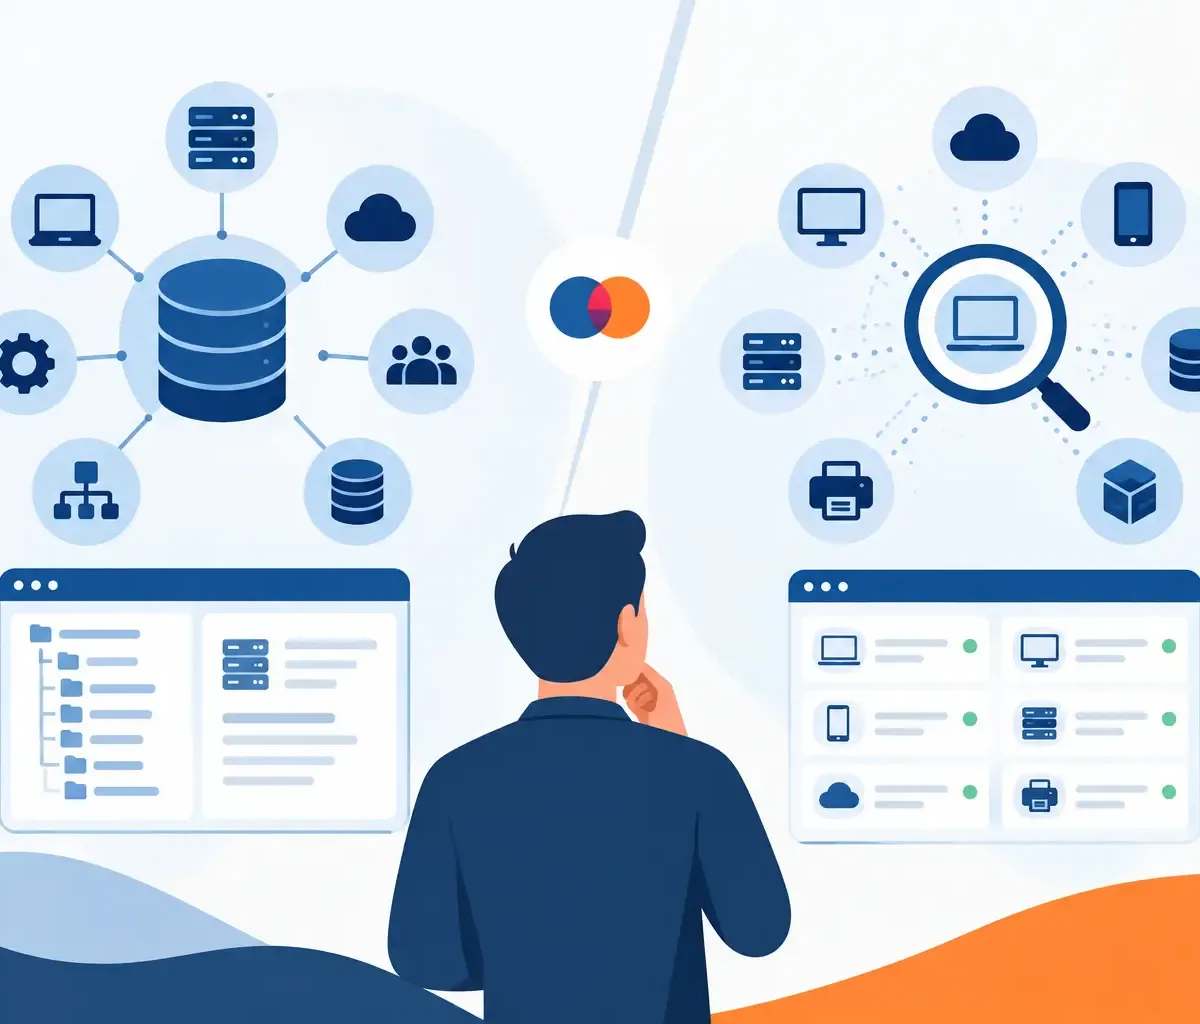
A critical service fails, and the immediate question is rarely “where is the asset record?” It is: what is affected, who owns it, what is exposed, and what must be restored first? The CMDB versus asset discovery discussion matters because these systems answer different parts of that question. Treating one as a substitute for the other leaves organisations with either an incomplete picture of reality or a large volume of technical data with too little operational meaning.
For regulated organisations, public-sector teams and managed service providers, the objective is not simply to maintain an inventory. It is to establish evidence that can support risk decisions, service resilience, audit responses and investment priorities.
CMDB versus asset discovery: the essential difference
A configuration management database, or CMDB, is intended to record configuration items and their relationships. A configuration item may be a server, application, cloud service, database, network device, business service, contract or dependency. Its value comes from context: a CMDB should show how technology supports a service and who is accountable for it.
Asset discovery identifies what is actually present in the environment. It finds devices, IP addresses, software, cloud resources, user identities and other connected or exposed entities. Depending on the method, discovery can also reveal configuration attributes, operating systems, network relationships, ownership clues and security posture.
The distinction is simple. A CMDB is a managed model of what the organisation believes it operates. Asset discovery is evidence of what exists and changes in the real environment. One provides intended structure and service context; the other tests that structure against operational reality.
Neither is sufficient alone. A CMDB without reliable discovery drifts into a record of assumptions. Discovery without a service model can generate an extensive list of assets but still struggle to explain which findings threaten payroll, patient care, production, citizen services or revenue.
Why CMDB records drift from reality
Most CMDB initiatives do not fail because the data model is wrong. They fail because keeping records current depends on manual updates, incomplete change processes and teams working across separate tools. A virtual machine can be created in minutes, a SaaS application can be adopted outside formal procurement, and a cloud identity can gain privileged access without appearing in the service records that matter to risk owners.
The result is familiar: duplicate entries, retired assets that remain in the database, active assets with no owner, and critical dependencies missing from impact assessments. During an audit or incident, teams then reconcile spreadsheets, ticketing records, cloud consoles and security tools under pressure.
Discovery reduces this gap by creating a recurring source of observed evidence. It can identify an unmanaged device, a newly exposed service or a configuration change that the CMDB does not yet reflect. That is not a criticism of the CMDB. It is the control that helps keep it trustworthy.
There is a trade-off. Discovery data is not automatically clean business data. A network observation may identify an endpoint but not its application owner, cost centre or importance to a business service. Organisations need rules to reconcile records, resolve duplicates and assign ownership rather than automatically accepting every observed attribute as authoritative.
What asset discovery should deliver
Basic discovery answers, “what is connected?” Mature asset discovery goes further. It should give teams a current view of the environment without relying solely on agents, periodic scans or self-reported records. That is particularly valuable in complex estates spanning on-premises infrastructure, Azure, AWS, Microsoft 365, Intune, Kubernetes and Active Directory.
For security leaders, the useful output is not a larger asset count. It is the ability to identify unknown assets, unauthorised exposure, unsupported systems, configuration weaknesses and vulnerable technology in the context of the services they affect. An internet-facing asset supporting a critical public service warrants a different response from a similar asset in an isolated test environment.
For operational teams, discovery should help validate dependencies and reveal changes before they become incidents. For compliance managers, it should create repeatable evidence that controls are operating across the actual estate, not only across assets recorded in a register months earlier.
An agentless and scanless approach can be especially effective where deploying endpoint software is difficult, network scanning is restricted, or service disruption is unacceptable. It also reduces the blind spots created when teams assume every asset has an agent installed and functioning. However, no collection method sees everything equally well. The right approach combines available telemetry, authoritative sources and clear validation processes.
The operating model: discovery feeds context
The strongest model is not “CMDB or discovery”. It is a continuous cycle in which discovery observes the estate, compares observations with managed records, and enriches those observations with ownership, service and risk context.
When a new device or cloud resource appears, the organisation should be able to determine whether it is expected, who owns it, what service it supports and whether it meets policy. When a known asset changes, the change should be assessed against its business impact. When an asset disappears, records should not remain indefinitely as false evidence of control.
This requires practical governance. Decide which source is authoritative for each data type. Human resources may be authoritative for employee identity, a cloud platform for resource creation, finance for lifecycle status, and the CMDB for approved service relationships. Discovery provides observed state and flags disagreement. It should not be asked to invent business ownership that the organisation has never assigned.
Teams should also define confidence levels. A relationship inferred from network traffic may be highly useful for investigation but require validation before it changes a formal service map. This avoids the two common extremes: ignoring discovered evidence because it is imperfect, or allowing unverified technical observations to overwrite carefully maintained records.
Prioritise by service impact, not asset volume
The commercial and security value of accurate asset intelligence comes from prioritisation. A thousand low-risk discrepancies should not distract teams from an exposed identity platform, a misconfigured cloud workload or an unsupported server supporting a critical service.
This is where CMDB context becomes operationally valuable. By associating assets and identities with business services, organisations can decide what needs fixing first. Vulnerability management, secure configuration, compliance assurance and resilience planning all become more credible when they are based on current discovery evidence and service impact.
Leadership does not need another dashboard reporting thousands of technical findings. It needs answers it can trust: which important business functions are exposed, what controls are failing, who is accountable, and what action will reduce risk. A well-maintained service model combined with continuous discovery can produce those answers faster and with less manual evidence gathering.
For MSPs and MSSPs, the same principle applies across multiple customers. Scalable discovery and normalised service context allow teams to deliver assurance outcomes consistently, rather than spending hours assembling reports from disconnected customer tools. The result is a clearer managed service, stronger customer conversations and less reliance on additional staffing to maintain visibility.
Where to start
Begin with the services that would cause the greatest operational, regulatory or financial impact if disrupted. Identify their owners, critical dependencies, supporting identities and expected technology footprint. Then compare that model with what discovery observes.
Do not wait for a perfect CMDB before improving visibility. Start by using discovered evidence to identify unknown, unmanaged and exposed assets around priority services. Resolve the highest-risk discrepancies, establish ownership rules, and make reconciliation part of normal operations rather than a pre-audit exercise.
Rebasoft supports this approach by bringing asset and service intelligence, exposure, configuration and assurance evidence into one operational view. The aim is not to create more records. It is to reduce cyber risk, improve audit and insurance readiness, and give leadership answers they can trust.
A CMDB becomes valuable when it reflects the environment people depend on. Asset discovery becomes valuable when it helps teams act on that reality. Connect the two around critical services, and visibility stops being an IT administration task and becomes a practical control for resilience.