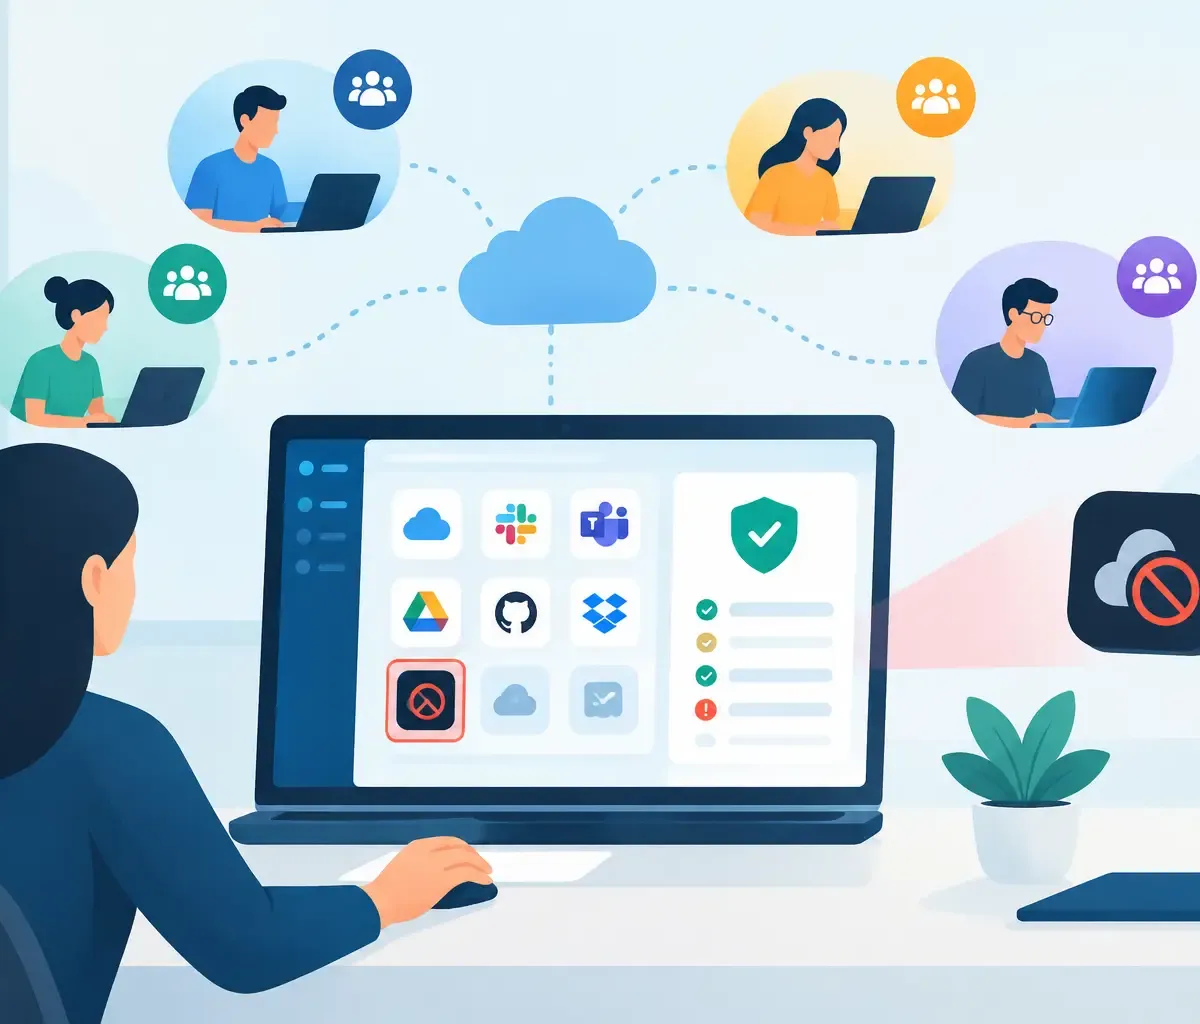
A finance team expensing an AI transcription tool, a project group sharing files through a personal workspace, and a developer connecting a cloud service to source code can each create material risk without ever raising a purchase request. Knowing how to monitor unauthorised SaaS is therefore not about catching employees out. It is about seeing which services hold business data, who can access them, and whether they support or weaken the controls your organisation relies on.
For regulated organisations, the issue extends beyond software spend. Unauthorised SaaS can bypass identity controls, data retention requirements, supplier assurance, monitoring, and incident response processes. It can also create a misleading picture for leadership: a security report may show strong control coverage while sensitive information is moving through services outside the approved estate.
Why unauthorised SaaS is a business risk
Shadow IT is often treated as a procurement problem. That framing is too narrow. Most employees adopt SaaS because it solves an immediate problem faster than the approved route: collaboration, automation, reporting, customer communication, document signing, or AI-assisted work. The business need may be legitimate. The risk lies in adopting the service without proportionate visibility and control.
A service can be low risk if it contains no company data, has no privileged connection, and is used by a small number of people. The same service becomes high risk when it stores customer records, synchronises identity data, receives payment details, or connects to Microsoft 365, Azure, AWS, Active Directory, a CRM platform, or source-code repositories.
That distinction matters because blanket bans rarely work. They drive use further out of sight and create friction for teams trying to deliver. A stronger approach identifies unauthorised SaaS, establishes its business context, and makes a deliberate decision: approve it, constrain it, replace it, or remove it.
How to monitor unauthorised SaaS without creating more noise
Effective monitoring begins with evidence from the environment rather than an annual employee survey or a static application register. Surveys have value, but they capture what people remember or choose to disclose. They do not reliably reveal connected applications, dormant accounts, personal tenants, unsanctioned integrations, or data movement.
Start by bringing together the signals already available across your estate. This should include identity-provider sign-in activity, secure web gateway or DNS records, firewall and proxy telemetry, cloud application logs, expense data, procurement records, endpoint information, and SaaS audit logs where they exist. No individual data source is complete. Combined, they provide a more credible view of services in use.
The key is to correlate these sources against users, departments, devices, and business services. A domain appearing in DNS data is only a clue. It becomes actionable when you can see that forty users in payroll access it, the service has an OAuth connection to Microsoft 365, and it is not on the approved supplier register.
A practical monitoring process should look for five types of signal:
- New SaaS domains and applications accessed by multiple users or departments.
- OAuth applications and API tokens granted access to email, files, calendars, identity directories, cloud platforms, or code repositories.
- Personal accounts used for business activity, particularly where corporate data may be uploaded or shared externally.
- Spend that does not map to an approved supplier, contract owner, data assessment, or renewal process.
- Services with elevated usage, sensitive data access, privileged permissions, or connections to critical business functions.
Avoid turning every unfamiliar application into an incident. Many will be harmless, already approved under a different supplier name, or used briefly for evaluation. Triage should be based on exposure and consequence, not simply on whether an application appears on a list.
Prioritise by data, access and business dependency
The fastest route to wasted effort is ranking unauthorised SaaS by the number of users alone. A widely used design tool with no sensitive data may deserve a simple review. A little-used application holding a mailbox permission or exporting HR records may require immediate action.
Assess each service against a small set of evidence-led questions. What data can enter the service? Which identities can log in, and are strong authentication controls enforced? What permissions or integrations does it hold? Does it support a critical process? Is there a named business owner? Has the supplier been assessed for security, privacy, resilience, and data location? Can access be removed quickly if the service is compromised?
This is where business-service context changes the quality of decision-making. An unauthorised service supporting a public-facing customer operation, clinical workflow, payment process, or operational technology environment should be assessed differently from one used for informal internal collaboration. Leadership needs to know what could fail, what would be exposed, and who owns the decision, not just how many applications have been discovered.
Establish an approval path people will use
Monitoring alone does not reduce risk. If the approved route takes weeks and offers no useful alternative, staff will continue to solve problems independently. A proportionate intake process gives teams a way to request a new service without creating unnecessary delay.
For lower-risk SaaS, this may be a short assessment covering purpose, data type, users, supplier details, and required integrations. Higher-risk services should trigger deeper due diligence, including contractual terms, information security review, privacy input, identity requirements, resilience expectations, and exit arrangements. The decision criteria should be clear enough that service owners understand what is required before they buy or connect a tool.
Create a defined outcome for every reviewed service. Approved services should have an accountable owner, documented data classification, access model, renewal date, and periodic review point. Restricted services may be permitted for a limited use case with conditions such as no customer data, no external sharing, or no privileged integration. Prohibited services need a reason that staff can understand, together with an approved alternative where possible.
This approach protects productivity while giving security, compliance, and procurement a shared operating model. It also creates evidence for auditors and insurers that the organisation does more than publish a policy.
Make identity and integration governance non-negotiable
Many of the most serious SaaS exposures begin with a seemingly routine consent screen. A user grants an application access to read mail, edit files, access contacts, or maintain access when they are offline. The application may be legitimate, but the permission is often broader and more persistent than the user realises.
Monitor consent grants, application registrations, service accounts, API keys, and tokens continuously. Establish which permissions require administrator approval and which can be granted by users. Review high-privilege applications routinely, especially those with access to collaboration platforms, identity systems, cloud subscriptions, finance data, or developer environments.
Offboarding matters here too. Removing a user from a corporate account does not necessarily cancel data held in a third-party SaaS tenant, revoke all API tokens, or close a personal account used for work. Your process should identify residual access and ensure the business owner can recover or delete company information when a service is retired.
Turn monitoring into measurable assurance
Security teams do not need another dashboard full of application names. They need a repeatable control that demonstrates improvement. Set measures that reflect both exposure and operational effectiveness: the number of discovered services, the proportion with a named owner, the number with sensitive data or elevated permissions, time to assess new services, and overdue reviews or renewals.
Report these measures by business unit and service criticality, not just as enterprise totals. This helps leaders see where demand is emerging and whether a particular function is relying on unmanaged tools to deliver important outcomes. It also makes conversations more constructive. The goal is not to assign blame; it is to fix the gap between business need and available technology.
For MSPs and MSSPs, the same model can be delivered across multiple customers without multiplying manual effort. A shared assurance process, with customer-specific policies and reporting, gives service providers a clearer way to evidence value and identify risk before it becomes an incident.
An agentless, scanless visibility approach can be particularly useful where endpoint coverage is incomplete, estates are hybrid, or deployment effort is constrained. Rebasoft can help correlate asset, identity, service, and exposure intelligence so teams can focus on the unauthorised SaaS that creates meaningful business risk rather than chasing every unfamiliar domain.
The most useful outcome is not a shorter list of applications. It is a leadership team that can answer a simple question with confidence: which cloud services support our critical work, which ones expose us, and what are we doing about them?