A device joins the corporate network, receives an address and reaches a critical service before anyone can confirm who owns it, whether it is managed, or whether it meets policy. That is the practical problem behind NAC versus zero trust. The debate is often framed as a replacement decision, yet the real issue is whether the organisation can make and prove sound access decisions across its network, cloud services and business-critical operations.
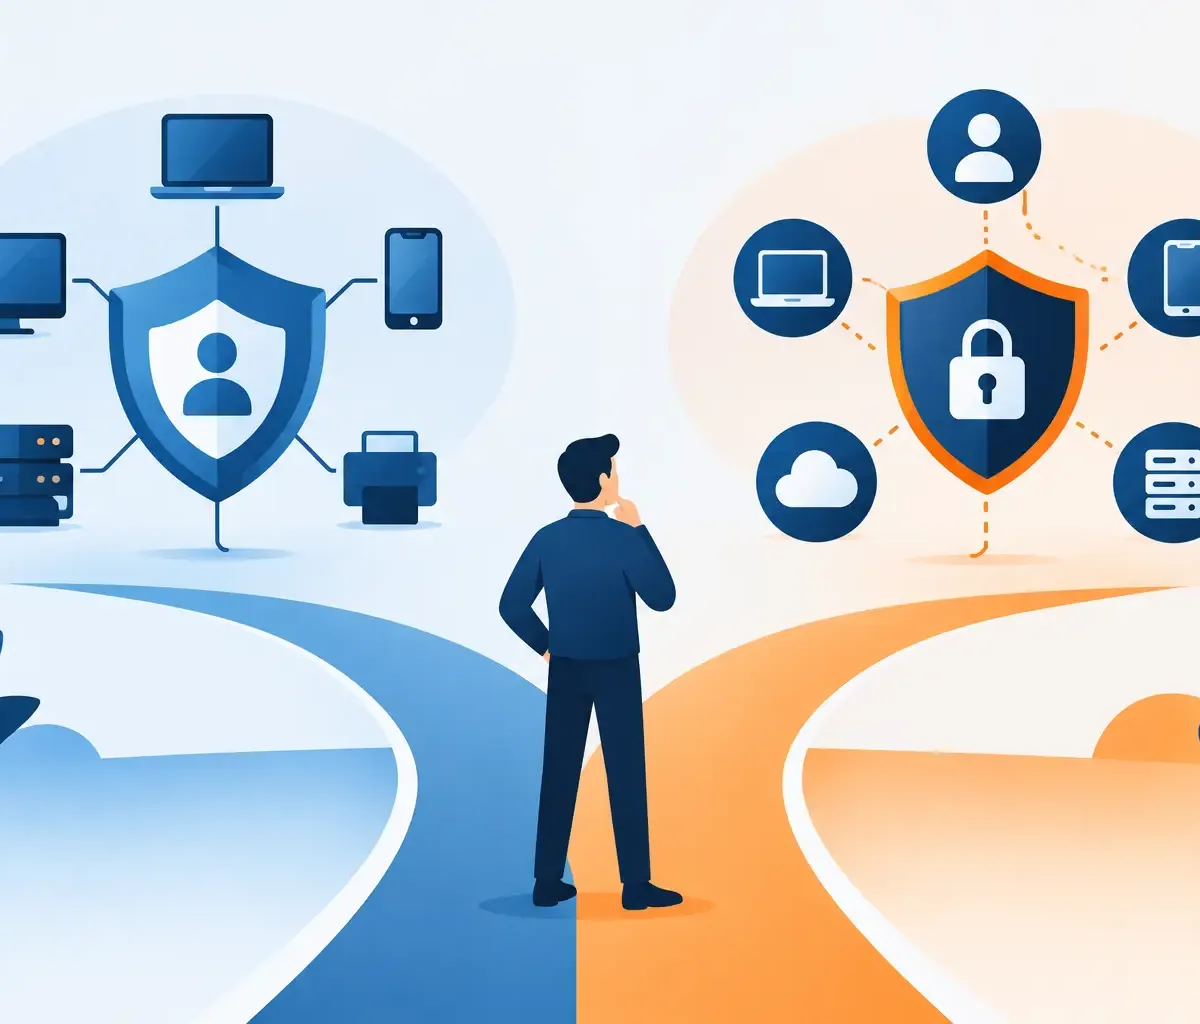
Network access control and zero trust address different parts of that problem. NAC governs access to the network. Zero trust governs access to applications, data and services through continuous verification and least-privilege principles. Treating one as a substitute for the other can leave material gaps in visibility, enforcement and audit evidence.
NAC versus zero trust: a false choice
NAC is an enforcement technology and policy framework focused on network admission. It can identify a device attempting to connect, assess defined conditions and permit, restrict, quarantine or deny access. In a campus, branch, operational technology environment or regulated estate with many unmanaged devices, that remains highly valuable.
Zero trust is a security model rather than a single product. Its central premise is that no user, device, workload or connection should receive implicit trust merely because it sits on an internal network. Access should be explicitly verified, limited to what is needed, and reassessed as risk changes.
The difference matters because a compliant device on the right VLAN is not automatically entitled to access every application. Equally, strong identity controls do not help much if an unknown device can connect to sensitive infrastructure without detection. NAC can control the front door to the network. Zero trust reduces the significance of being inside the building.
For many organisations, the answer is not to choose between them. It is to decide where each control produces the greatest reduction in business risk, then ensure both operate from reliable evidence.
What NAC still does well
NAC is at its strongest where physical and network connection are meaningful security boundaries. This includes hospitals, manufacturing sites, public-sector estates, education networks, offices with extensive guest access, and environments where IT and operational technology coexist.
Control the point of connection
A well-designed NAC deployment can distinguish between corporate endpoints, contractor devices, printers, medical equipment, building-management systems and unknown assets. It can apply different network policies based on identity, device type, location and security posture.
That matters when a device cannot support an endpoint agent or modern identity integration. Legacy systems, specialist operational technology and internet-connected equipment are common in high-consequence environments. They still need to be identified, segmented and monitored, even where traditional endpoint controls are impractical.
NAC can also reduce the operational impact of poor asset hygiene. If a device has no known owner, fails a required configuration check or appears on an unexpected network segment, access can be limited while the issue is investigated. This gives security teams a practical control where spreadsheets and periodic scans offer only hindsight.
Where NAC falls short
NAC policy can become difficult to maintain when it depends on incomplete asset inventories, unreliable device profiling or network designs that have evolved without clear ownership. A device might be admitted because it looks like a permitted class of equipment, while its associated service, vulnerability status or business importance remains unknown.
NAC also does not inherently control access after a user reaches cloud applications or software-as-a-service platforms. Once work moves beyond the traditional network perimeter, the value of network location declines. That does not make NAC obsolete. It means NAC must be part of a broader control strategy.
What zero trust changes
Zero trust shifts the access question from Can this user connect to the network? to Should this identity, using this device, have this level of access to this service right now?
In practice, this involves strong identity assurance, multi-factor authentication, conditional access, device posture, least privilege, application segmentation and monitoring of anomalous behaviour. Access decisions can take account of the user, device health, authentication strength, location, sensitivity of the service and current risk signals.
The business benefit is reduced lateral movement and tighter control over high-value services. A compromised user account should not create broad access simply because it authenticated successfully. A contractor may need a specific application for a defined period, not a route into the wider environment.
Zero trust is particularly relevant for organisations with hybrid work, cloud platforms, third-party access and distributed services. It can improve resilience by protecting the applications and data that support revenue, public services or patient care, rather than relying on a network boundary that no longer reflects how work is done.
Zero trust is not a product switch
The term can create false confidence. Buying a zero trust-labelled technology does not establish zero trust if identity records are inaccurate, privileged access is poorly governed, device ownership is unknown or critical services have not been mapped.
A policy may correctly block a risky sign-in, but leadership still needs answers: Which service would be affected? Is the user supporting a critical process? Does the device have known vulnerabilities? Is there an approved exception? Can the organisation show an auditor that the control worked consistently?
Without that context, access policies may become either too permissive or too disruptive. Both outcomes carry cost. Excessive restrictions interrupt operations and drive workarounds. Weak conditions leave valuable services exposed.
The visibility gap that undermines both
The most common failure is not choosing the wrong acronym. It is making access decisions using partial, stale or disconnected information.
NAC needs an accurate view of what is connected and where. Zero trust needs confidence in identity, device state and the services being accessed. Vulnerability management needs to know which weaknesses affect assets that support important business functions. Compliance teams need evidence that controls are operating, not screenshots collected shortly before an audit.
These requirements are closely connected, but many organisations manage them through separate tools, teams and reporting cycles. One platform reports devices, another identities, another vulnerabilities, another cloud configuration and another service desk data. The result is alert volume without a defensible view of priority.
Continuous asset and service intelligence changes that position. It establishes a current record of devices, users, connections, configurations and service dependencies, then relates technical findings to the business services that matter. This enables teams to focus on a vulnerable device connected to a critical service before spending time on a low-impact issue elsewhere.
Agentless and scanless visibility can be especially useful where deployment windows are limited, assets are fragile or endpoint coverage is inconsistent. It reduces dependence on every device being able to run an agent and helps expose the unmanaged systems that often sit outside conventional security reporting.
Choose controls by business outcome
A sensible decision begins with the environments and risks that need to be controlled. If the immediate concern is unknown equipment joining a sensitive network, NAC should be a priority. If the main exposure is excessive access to cloud applications, privileged accounts or remote services, identity-led zero trust controls may deliver faster risk reduction.
Most established organisations need both, applied proportionately. The following questions help define the order of work:
- Which business services would suffer most if access was abused or disrupted?
- Which networks contain unmanaged, legacy or operational technology assets?
- Can the organisation identify the owner, security state and service dependency of every connected asset?
- Are access decisions based on current evidence, or on assumptions embedded in old network rules?
- Can teams demonstrate that exceptions, privileged access and segmentation controls are reviewed and effective?
The answers should shape investment. A hospital may prioritise network segmentation and device visibility around clinical equipment, while strengthening zero trust controls for remote administration and cloud collaboration. A financial services organisation may focus first on identity governance and privileged access, while using NAC to constrain contractor and branch-office connectivity.
Build an operating model, not another silo
NAC and zero trust generate value when ownership is clear. Network teams need workable policies and minimal disruption. Security teams need enforceable controls and evidence. Service owners need to understand how access decisions affect availability. Compliance teams need continuous assurance rather than a manual exercise at audit time.
This is where consolidation matters. A common intelligence layer can connect network access, identity visibility, configuration status, vulnerabilities and business-service context. Rather than asking each team for a separate report, leadership can see what is connected, what is exposed, which controls are working and what needs fixing first.
Rebasoft supports this approach by bringing asset, service, identity and control evidence into one operational view, helping teams prioritise remediation against the services that matter most. For MSPs and MSSPs, the same model can provide consistent, multi-customer assurance without adding a separate point tool for every requirement.
Start with evidence, not a product decision
Before expanding NAC or launching a zero trust programme, establish a baseline. Identify connected assets, map critical services, validate identity sources, assess existing segmentation and document where access is granted by assumption rather than verified conditions. This reveals whether the immediate problem is weak enforcement, poor visibility or both.
The best next step is usually the one that gives leadership answers they can trust while reducing exposure around the most important services. When every access decision can be tied to current evidence and business impact, NAC and zero trust stop competing for budget and start working as complementary controls.